Cloud Security Engineering

Surya Naga Sesank M

Security Architecture DevSecOps

Senior cloud security engineering with 10+ years in cybersecurity, across AWS, Microsoft Azure, and Google Cloud. Focused on Terraform, IAM, Zero Trust, detection, incident response, security automation, and governance.

AWS Microsoft Azure Google Cloud Terraform
AWS IAM Microsoft Entra ID Zero Trust Workload Identity

  • Credential 01

    10+ Years Cybersecurity

  • Credential 02

    AWS Certified Solutions Architect - Associate

  • Credential 03

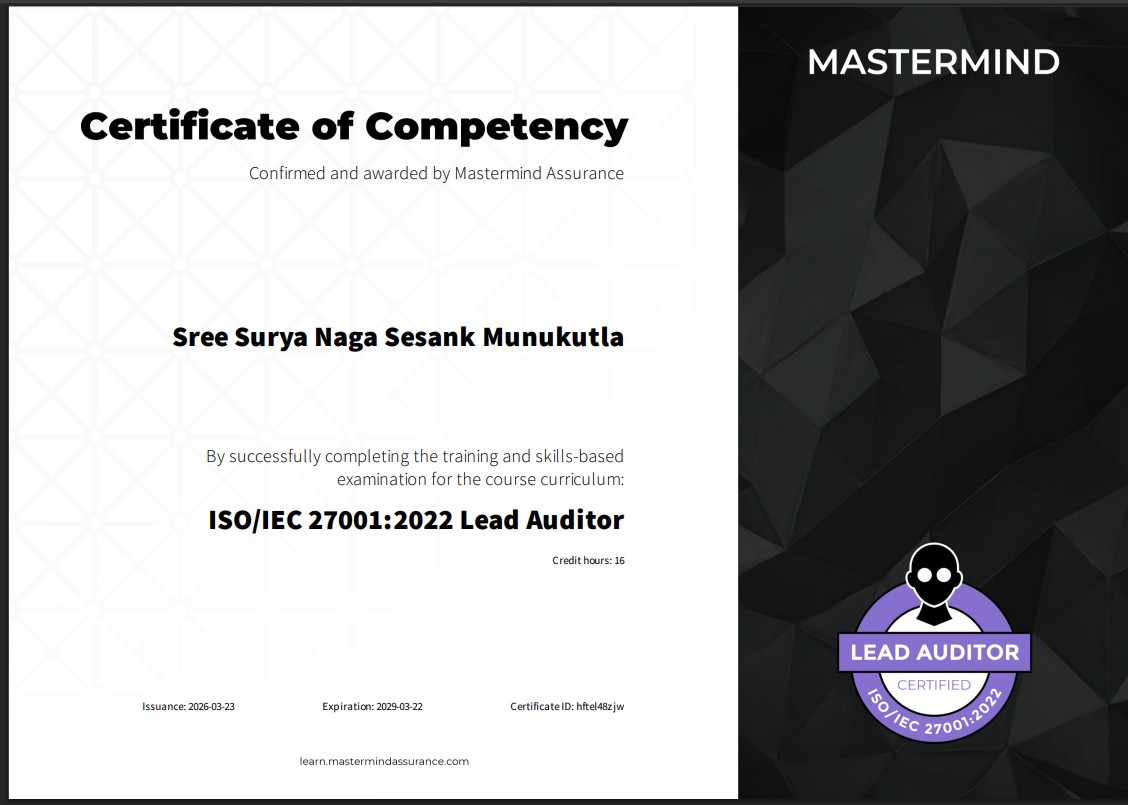
    ISO 27001 Lead Auditor

  • Credential 04

    CEH

  • Credential 05

    AWS Well-Architected Foundations

01

Architecture

Security architecture and governance

02

Infrastructure

Terraform and Infrastructure as Code

03

Identity

AWS IAM / Microsoft Entra ID / Zero Trust / Workload Identity

04

Response

Detection and incident response engineering

Featured engineering record

Current security engineering focus

Status: Validated

FEATURED PROJECT / Cloud identity security

AZ-01 β€” Azure Workload Identity Attack & Secretless Federation Lab

A validated Azure lab tracing a deliberately vulnerable long-lived workload credential and excessive RBAC through controlled attack validation, secretless federation remediation, revalidation, and verified teardown.

Results apply only to tested actions and known project-owned targets. Baseline and remediated deployments used separate validation windows; the retired credential was not replayed in place. The Azure environment is destroyed. This lab does not establish universal least privilege, penetration-test coverage, production suitability, or broader Azure security assurance.

Engineering evidence

Objective
Validate a bounded workload identity attack path and remediate credential and authorization risks using secretless federation and reduced Azure RBAC scope.
Delivery
Terraform, controlled Azure CLI validation, and GitHub Actions static security CI
Validation record
Sanitized baseline, attack, federation, post-remediation, teardown, and CI validation records

Controls in scope

  • Microsoft Entra ID
  • Azure RBAC
  • GitHub OIDC
  • Workload Identity Federation
  • Terraform
  • Least privilege

Core security capabilities

Cloud security capability stack.

A senior engineering stack organized around architecture, control implementation, and evidence-oriented practice rather than generic technology keywords.

STACK-01

Cloud Platforms

Cloud security engineering across AWS, Microsoft Azure, and Google Cloud.

  • AWS
  • Microsoft Azure
  • Google Cloud

STACK-02

Infrastructure Engineering

Reviewable infrastructure delivery and automation practices.

  • Terraform
  • Infrastructure as Code
  • Git workflows

STACK-03

Identity & Zero Trust

Identity-centered access control and accountable cloud boundaries.

  • AWS IAM
  • Microsoft Entra ID
  • Azure RBAC
  • Workload Identity Federation
  • Permission boundaries
  • SCPs
  • Zero Trust

STACK-04

Detection & Incident Response

Detection requirements and response architecture with human review where needed.

  • CloudTrail
  • GuardDuty
  • EventBridge
  • Investigation

STACK-05

Application & Edge Security

Layer 7 protection and network security controls across cloud environments.

  • AWS WAF
  • Google Cloud Armor
  • Network security

STACK-06

Security Architecture & Governance

Control boundaries, multi-account architecture, and framework-aware engineering context.

  • Governance controls
  • NIST
  • ISO 27001
  • HIPAA/HITRUST-aligned engineering
  • PCI DSS
  • SOC 2

STACK-07

Engineering Practice

Evidence-oriented delivery that distinguishes implementation, validation, and current state.

  • DevSecOps
  • Automation
  • Controlled validation
  • Remediation
  • Revalidation
  • Documentation

Engineering projects

Flagship project records

Evidence-backed cloud security engineering case studies with traceable objectives, controls, delivery methods, and validation records.

PROJECT-01

Validated

Web application protection

Enterprise Multi-Cloud WAF Evaluation Platform

Compare equivalent AWS WAF and Google Cloud Armor deployments through reusable Terraform.

Platform scope
AWS / Google Cloud
Delivery
Modular Terraform with environment configuration

Key controls

  • AWS WAF
  • Cloud Armor
  • IAM
  • Network security

Evidence: Deployment, validation, and lifecycle documentation

2 Published Articles

PROJECT-02

In Progress

Incident response automation

AI-Powered Polycloud Security Incident Response Platform

Prepare an AWS-first, AI-assisted incident response architecture for reviewable Terraform delivery.

Platform scope
AWS
Delivery
Terraform-first repository and reusable module design

Key controls

  • CloudTrail
  • EventBridge
  • IAM
  • Human review

Evidence: Phase documentation and evidence mapping

PROJECT-03

Active Engineering

Cloud governance

AWS Multi-Account Zero-Trust Architecture Lab

Design and validate a secure multi-account AWS landing zone with preventative and detective controls.

Platform scope
AWS / AWS Organizations
Delivery
Terraform-managed organizations and policies

Key controls

  • SCPs
  • CloudTrail
  • GuardDuty
  • Permission boundaries

Evidence: AWS CLI tests, CloudTrail logs, and drift checks

3 Published Articles

PROJECT-04

In Progress

Healthcare security engineering

HIPAA/HITRUST-Aligned Healthcare Security Engineering Platform

Implement security controls for a synthetic healthcare workload aligned to selected HIPAA and HITRUST control objectives.

Platform scope
AWS / Google Cloud
Delivery
Terraform with AWS CLI and console validation

Key controls

  • Network segmentation
  • Least privilege
  • VPC Flow Logs
  • CloudWatch

Evidence: Validation, remediation, and teardown records

PROJECT-05

Validated

Cloud identity security

AZ-01 β€” Azure Workload Identity Attack & Secretless Federation Lab

Validate a bounded workload identity attack path and remediate credential and authorization risks using secretless federation and reduced Azure RBAC scope.

Platform scope
Microsoft Azure / Microsoft Entra ID / GitHub Actions
Delivery
Terraform, controlled Azure CLI validation, and GitHub Actions static security CI

Key controls

  • Microsoft Entra ID
  • Azure RBAC
  • GitHub OIDC
  • Workload Identity Federation
  • Terraform
  • Least privilege

Evidence: Sanitized baseline, attack, federation, post-remediation, teardown, and CI validation records

PROJECT-06

In Progress

Azure security architecture

AZ-02 β€” Azure Cloud Security Architecture Review & Controlled Remediation Lab

Develop an Azure cloud security architecture review and controlled remediation lab.

Platform scope
Microsoft Azure
Delivery
In progress; delivery details pending publication

Key controls

Control scope pending publication

Evidence: Validation evidence pending publication

View case studyRepository pending

Security Labs & Project Series

Working notes from hands-on security labs

A lower-hierarchy series of public engineering write-ups. These records complement, rather than replace, the four flagship case studies above.

  1. LAB 01

    Hashnode / Jan 2026

    πŸ” Project 1: Building a Secure Cloud Baseline in AWS (Before Things Break)

    Read article
  2. LAB 02

    Hashnode / Jan 2026

    πŸ” Project 2: Security Design Trade-offs in AWS (Where Convenience Starts to Win)

    Read article
  3. LAB 03

    Hashnode / Jan 2026

    πŸ” Project 3: Implementing and Testing Security Controls in a Real Cloud Environment

    Read article
  4. LAB 04

    Hashnode / Jan 2026

    πŸ” Project 4: Eliminating SSH with AWS Systems Manager β€” IAM-Controlled, Auditable EC2 Access

    Read article
  5. LAB 05

    Hashnode / Feb 2026

    πŸ” Project 5: Zero-Trust EC2 Access in AWS Using IAM, SSM, CloudTrail, and GuardDuty

    Read article
  6. LAB 06

    Hashnode / Feb 2026

    πŸ” Project 6: Implementing Just-In-Time (JIT) SSH Access for EC2 on AWS

    Read article
  7. LAB 07

    Hashnode / Feb 2026

    πŸ”Project 7: Automated Threat Containment in AWS – Building a Cloud-Native SOAR Workflow

    Read article
View All Engineering Writing

Engineering evidence

Senior cloud security engineering, designed to be reviewed.

With 10+ years in cybersecurity, the work centers on cloud security architecture, infrastructure automation, identity, governance, detection, and incident-response engineering. Supporting records emphasize practical controls, validation, and clear limits.

Engineering scope

  • AWS / Microsoft Azure / Google Cloud
  • Terraform / Infrastructure as Code
  • AWS IAM / Microsoft Entra ID / Zero Trust
  • Detection / Incident Response
  • DevSecOps / Security Automation
  • Governance / Security Assurance

Framework familiarity includes NIST, ISO 27001, HIPAA/HITRUST-aligned engineering, PCI DSS, and SOC 2. This familiarity describes engineering context only and does not imply certification, compliance, or attestation.

Evidence-oriented method

  1. 01

    Model

    Define the control objective, cloud boundary, and assumptions before implementation.

  2. 02

    Implement

    Use infrastructure-as-code and versioned artifacts where the project supports them.

  3. 03

    Validate

    Test controls, record results, and distinguish confirmed evidence from planned work.

  4. 04

    Explain

    Document architecture, limitations, and remediation paths so the work can be reviewed.

Professional Credentials

Certifications & Credentials

Industry-recognized certifications validating expertise across Cloud Security, Cybersecurity, Architecture, Governance and Enterprise Security Practices.

Featured
ISO 27001 Lead Auditor
Lead Auditor

ISO 27001 Lead Auditor

AWS Certified Solutions Architect – Associate
AWS Certification

AWS Certified Solutions Architect – Associate

EC-Council Certified Ethical Hacker (CEH)
Security Certification

EC-Council Certified Ethical Hacker (CEH)

AWS Well-Architected Foundations
AWS Training

AWS Well-Architected Foundations

Contact

Let's Build Secure Cloud Solutions Together

I'm always interested in discussing Cloud Security, Security Architecture, DevSecOps and Infrastructure as Code opportunities.